

SEOSeptember 23, 2026 · 10 min read
Rehab SEO Cost: What Treatment Centers Pay and What It Covers
Ethan Sweet
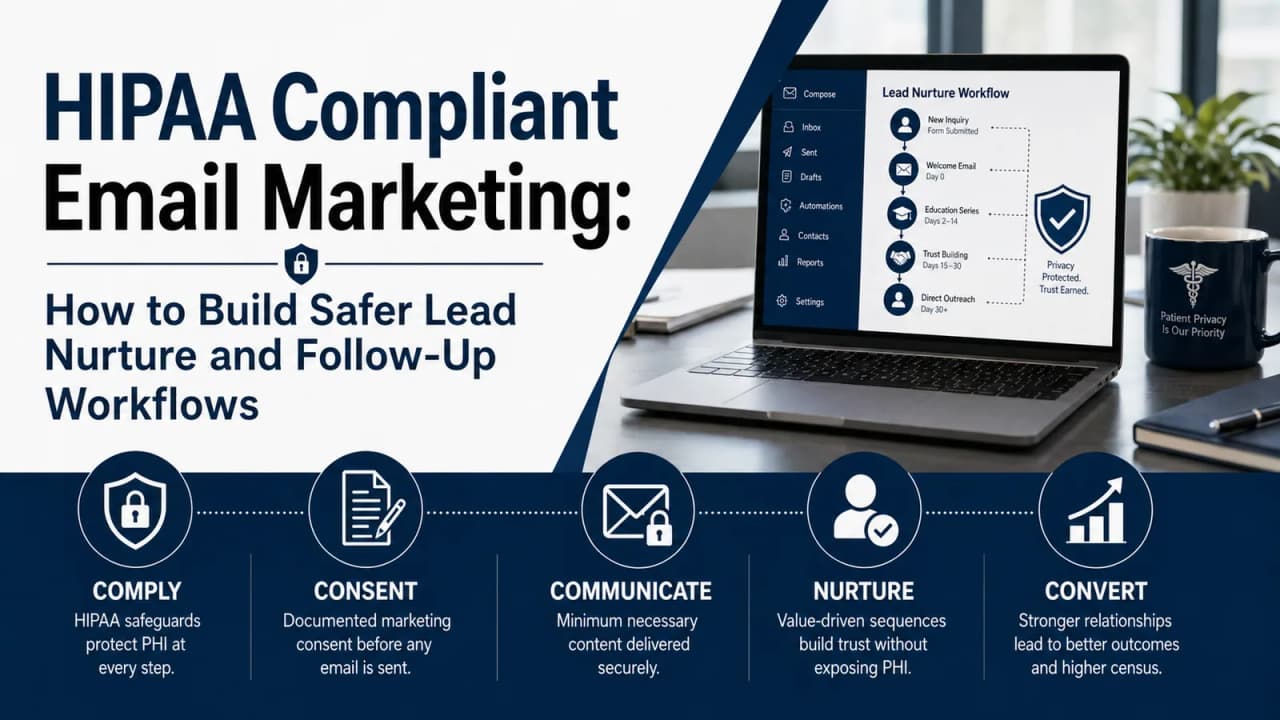
HIPAA sets three questions for every marketing email a treatment center sends.
Under the Privacy Rule, a covered health care provider needs a person's written authorization before it uses their protected health information for marketing. HHS's definition of marketing, though, leaves out most messages a program sends about its own services, and that changes what your list and your vendors need.
For a rehab or mental health program, HIPAA compliant email marketing comes down to three questions. Is the email marketing under the Privacy Rule, does every vendor that holds the list have a business associate agreement (BAA), and does the message itself reveal more than it should?
Substance use programs have a fourth question, because 42 CFR Part 2 adds its own consent rules. Each question is answered below with a link to the regulation or the HHS page it comes from, and none of this replaces advice from healthcare counsel.
The Privacy Rule, at 45 CFR 164.501, defines marketing as a communication about a product or service that encourages the recipient to buy or use it. If an email meets that definition and uses patient information, 45 CFR 164.508 requires the person's authorization first.
The same definition carves out three kinds of communication. An email is generally not marketing when it describes a health-related service your own organization provides, when it is for the person's treatment, or when it is for case management, care coordination, or recommending other treatment settings.
Those carve-outs disappear when a third party whose product is described pays you to send the message. HHS also says a covered entity may not sell lists of patients to third parties without authorization from each person on the list.
| Marketing under HIPAA? | Why | |
|---|---|---|
| Alumni event invitation sent by your program | Usually not | It describes your own health-related service |
| Newsletter announcing your new IOP evening track | Usually not | It describes a service your organization provides |
| Admission-day logistics to a confirmed patient | No | It is part of the person's treatment |
| Promotion for a partner program that pays you to send it | Yes | A third party is paying for the communication |
| Selling or sharing your list with another company for its own offers | Yes | HHS says patient lists can't be sold without each person's authorization |
A partner that pays a treatment center to promote a recovery home or lab raises a second issue. EKRA makes it a federal crime to pay or receive remuneration for referrals to recovery homes, clinical treatment facilities, and labs, so any paid arrangement belongs with counsel first.
When an email does need authorization, 45 CFR 164.508 lists the core elements. The form describes the information to be used, who will use it, who will receive it, the purpose, an expiration date or event, and the person's signature and date.
It must also tell the person they can revoke it in writing, and it must say so when a third party is paying for the marketing. Keep signed authorizations for six years, which 45 CFR 164.530(j) sets as the retention period for required documentation.
42 CFR Part 2 protects records that would identify a person as having a substance use disorder, when those records come from a federally assisted program. Federal assistance is defined broadly and includes Medicare participation, a federal registration to dispense controlled substances for substance use treatment, federal funding, and federal tax-exempt status.
Part 2 generally requires the patient's written consent before records are used or disclosed, and section 2.31 lists what that consent must include. For an alumni or newsletter list built from patient records, have counsel confirm how Part 2 applies to your program before the first send.
The simplest safeguard is a separate, plainly worded opt-in at discharge for alumni email. It gives you a clear record of what each person agreed to receive, and it keeps the email list apart from the clinical record.
A business associate is a person or company that creates, receives, maintains, or transmits PHI on behalf of a covered entity. HHS lists a cloud service provider that stores or processes electronic PHI among its examples, which fits an email platform that stores patient or inquiry contacts for you.
A list of people who called a treatment center, filled out an inquiry form, or completed treatment is health information about each of them. Treat that list as PHI, and get a signed BAA from the email platform, the CRM that feeds it, and any tool that syncs between them.
Under 45 CFR 164.504(e), the BAA must describe what the vendor may do with the PHI and bar other uses. A business associate must also have a BAA with any subcontractor that handles the PHI, so ask each vendor which subcontractors touch your data.
Confirm that the agreement covers the specific product and features you plan to use, including marketing email, forms, and text messaging. A BAA that covers one product from a vendor does not automatically cover everything else that vendor sells.
HHS says providers may email patients if they apply reasonable safeguards, such as checking the address before sending and limiting the amount or type of information in unencrypted email. Patients can also ask to be contacted by other means, and HHS says a provider should accommodate a reasonable request.
Encryption is not mandatory under the current Security Rule, and skipping it still takes a documented decision. HHS calls it an addressable specification, which means you implement it when a risk assessment finds it reasonable, or you document why not and use an equivalent measure.
The Privacy Rule's minimum necessary standard points the same way. Use only the information a message needs, and marketing email rarely needs any health detail at all.
RELATED READING
The unsubscribe rules come from the CAN-SPAM Act, which the FTC enforces for all commercial email. The FTC's guide lists accurate header information, a subject line that matches the content, a clear disclosure that the message is an ad, and a valid physical postal address.
Every commercial email also needs a clear way to opt out, and the FTC says you must honor an opt-out within 10 business days. Apply the suppression list to every tool that sends email for you, including tools other than the one where the person clicked unsubscribe.
Most treatment centers need four email streams, and each one has a different consent basis. Keep them in separate lists, so a family who asked for a callback never lands on an alumni newsletter.
| Stream | Who receives it | Consent basis | What it can say |
|---|---|---|---|
| Inquiry follow-up | People who contacted admissions | Their request for contact | A confirmation and a named callback number |
| Family education | Inquirers who opted in to more information | A separate opt-in | General articles on assessment, insurance, and admission |
| Alumni updates | Former patients who opted in at discharge | Written opt-in, plus Part 2 review for SUD programs | Events, groups, and program news |
| Referral partners | Therapists, psychiatrists, and other referrers | Business relationship | Program updates with no patient information |
For the timing and task side of those workflows, see our guide to healthcare marketing automation. For forms, pixels, and CRMs, see our piece on keeping health data out of marketing tools.
Behavioral health billing and RCM firms are often business associates of the treatment centers they serve. Their marketing email goes to operators and CFOs, which is B2B email with no PHI, but client patient data can never feed it, because a BAA limits the business associate to the uses it allows.
Toxicology labs are in the same position when they email program directors. Telehealth and psychiatry practices are usually covered entities themselves, so the marketing definition, BAA, and content rules above apply to their patient email directly.
Adjacent companies can still build a strong list from operators who opt in. Cipher Billing pairs 55 billing and RCM articles with LinkedIn publishing, which gives its email and sales outreach something useful to send.
Under HIPAA, usually not, because a message about your own services is generally excluded from the marketing definition. Substance use programs should also check Part 2 with counsel, and every commercial email still needs a CAN-SPAM opt-out.
Encryption is an addressable specification under the Security Rule, so you implement it or document an equivalent measure. For marketing email, the simpler protection is keeping health details out of the message.
Yes, if it stores or sends a list of patients or inquirers for you. Confirm that the BAA covers the product and features you will actually use.
Google's personalized advertising policy does not allow Customer Match for health and mental health services. Sharing patient contacts with an ad platform also raises HIPAA marketing and BAA questions, so treat it as off-limits.
HIPAA requires covered entities to keep signed authorizations and other required documentation for six years. Keeping opt-in and opt-out records for the same period makes any later question easier to answer.
If you want your email, forms, and CRM reviewed before your next campaign, our treatment center web design team will check every tool that touches inquiry data and send a written report within 5 business days. Book a strategy call to set up that review.
About the author

Ethan founded Sweet Media to give behavioral health facilities an agency that speaks the language of treatment — and measures success in admissions, not impressions.
CONNECT ON LINKEDINIn this article
Tags
CONTINUE READING
SEOSeptember 23, 2026 · 10 min read

BlogJuly 14, 2026 · 13 min read

Paid MediaMay 14, 2026 · 13 min read
Social MediaApril 28, 2026 · 10 min read
SEOApril 28, 2026 · 9 min read
Paid MediaApril 28, 2026 · 9 min read
MORE FROM COMPLIANCE
VIEW ALL
Ready to grow?
Sweet Media builds search and ads programs for addiction treatment and mental health providers. Book a free strategy call to see how these ideas apply to your facility.